During the past year, the cybercrime group ShinyHunters has been extorting companies and, last week, took over a rival gang’s leak site. Now, it has gone after the agency that warned the public about it. The FBI stated on Tuesday that it is investigati…
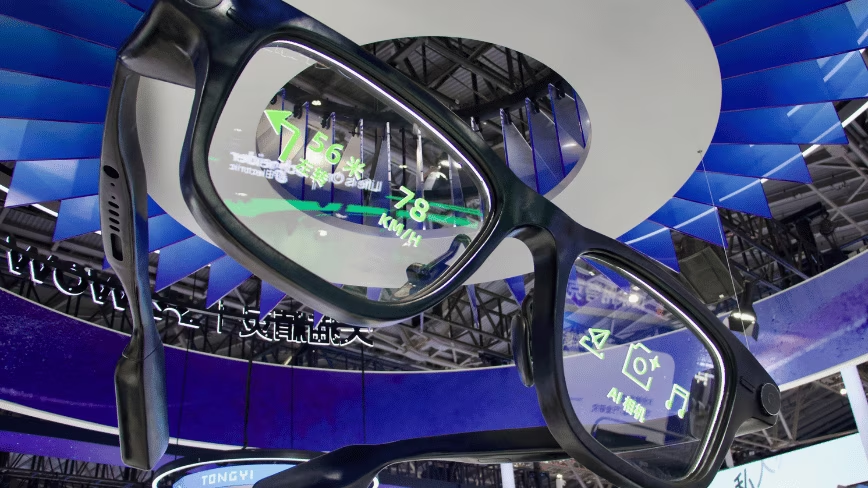
Smart glasses may look cool but there’s absolutely no place in our schools or classrooms for them. Sabine Winton said that on Tuesday. Western Australia’s education minister was announcing what she called the country’s most comprehensive ban on the dev…
Security can no longer stop at protecting the person behind the screen. It has to extend to the agent itself acting on their behalf. Ciprian Istrate said that on Tuesday. He runs consumer operations at Bitdefender, and the Romanian company was launchin…
They need to trust what AI agents can see and do before they can scale them. Yotam Segev said that on Tuesday, about what the Global 2000 keeps telling his company. The Cyera cofounder and chief executive was announcing a $400m investment from Growth E…
That access should enable assessors to challenge our assumptions, identify risks we may have missed, and reach their own conclusions about the effectiveness of our safeguards. OpenAI published that on Tuesday, in a document setting out what it wants ou…
While the CAC summoned all 7 companies namechecked by Anthropic’s report, the probe quickly zeroed in on DeepSeek and Moonshot due to the examples the report detailed. Jing Yang wrote that on Tuesday, about her own story. She and Qianer Liu reported fo…
In response to the ZCode product security issues reported by the community, we have completed the necessary remediation and sincerely apologize to all our users. Z.ai posted that on Monday, on ZCode’s official account. The Beijing company, formerly Zhi…
Amazon fought AI shopping agents on two fronts on Monday. It blocked Muse, Meta’s new AI assistant, from Amazon.com. It also filed an amended complaint against Perplexity, accusing the company of misleading a federal appeals court. The block came first…
“It’s about whether the lights stay on and the water stays safe when an adversary attacks,” said Dmitri Alperovitch, the CrowdStrike co-founder who is returning to the board of Dragos. The industrial cybersecurity company said on Monday it has closed i…
The AI industry already knew attackers could poison plugin marketplaces. Its answer was to lock every plugin to one reviewed version of its code. That lock is what just broke. Researchers at Air Security published a vulnerability on Thursday that they …